
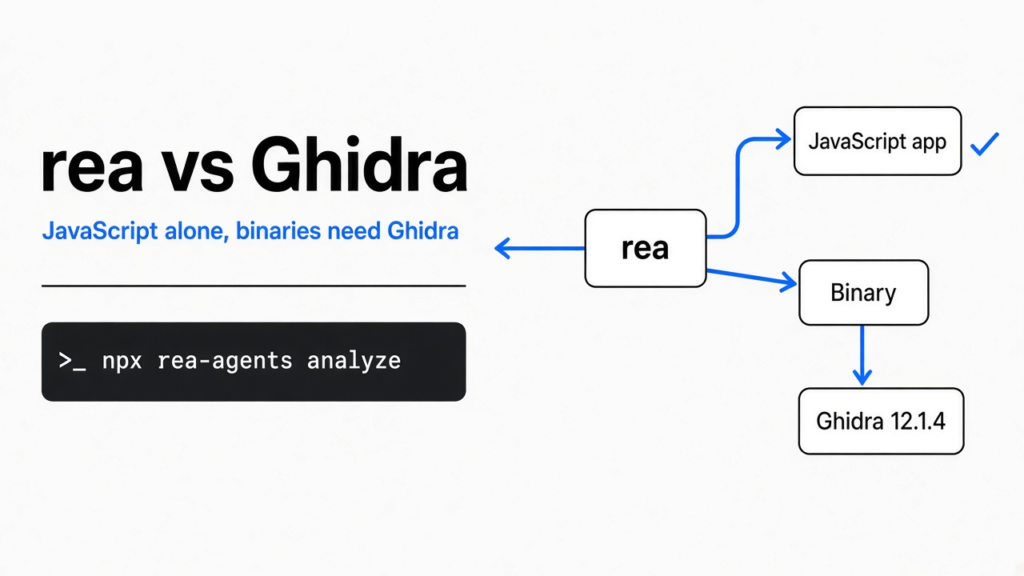

Most people meet rea as “the thing that lets a coding agent drive Ghidra”, and then stop when Ghidra isn’t installed. On a fresh Linux box with no Ghidra, Hopper, IDA or Kuna, I found that rea 6.9.0 still did useful work on compiled files. It just wasn’t the work its analyze command promises.
This is a guide to that middle ground: what rea can tell you about a binary on its own, where it hands off to a decompiler, and how to read its answers without over-trusting them.
The rea Tool Grew Fast Since October
When this post first went up in October, npx rea-agents --help printed version 4.0.1 with 69 commands. On 18 November 2026 the same command printed rea@6.9.0, and rea doctor reported 196 CLI commands and 255 MCP tools. New families cover Android packages, firmware, Electron fuses, web captures, debuggers and desktop app capture.
The doctor check changed too. In October it marked a Debian 12 host as unsupported. Today, on Debian 13 with Node 24.22.1, the node and host checks passed. Every decompiler engine still showed as missing, with one line each telling you what to set: GHIDRA_INSTALL_DIR for an extracted Ghidra 12.x release at 12.1 or later, HOPPER_LAUNCHER_PATH for Hopper, REA_IDA_MCP_CONFIG for IDA and REA_KUNA_COMMAND for Kuna.
Which rea Commands Work With No Decompiler
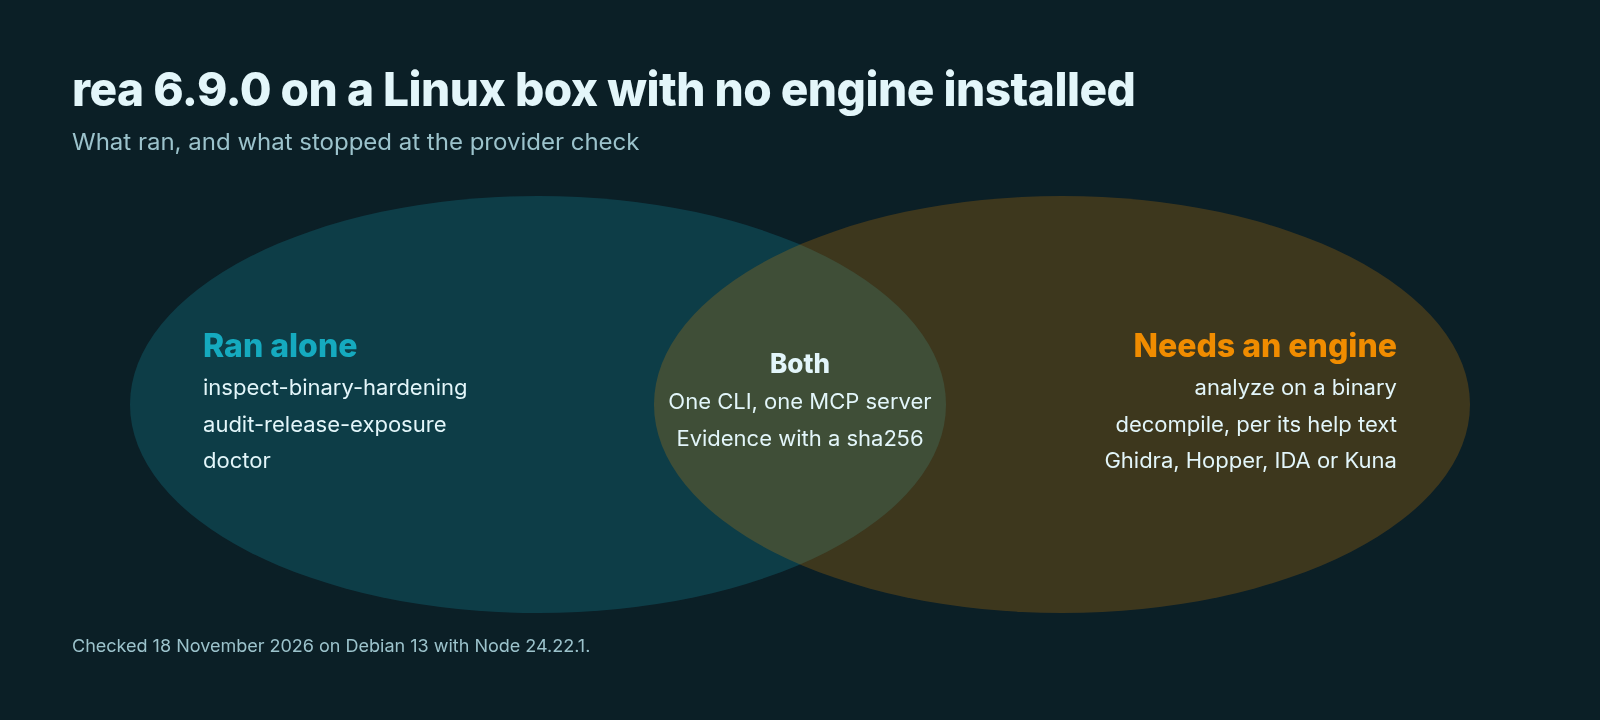
The ones that parse file headers directly. I ran inspect-binary-hardening on two Linux executables: /usr/bin/bwrap from the distro, and a Go binary I’d built from source the same day.
npx -y rea-agents@6.9.0 inspect-binary-hardening /usr/bin/bwrap --format json
Each row in the result comes with a state, a confidence level and the evidence it was based on, down to the byte offset.
| Property | bwrap (distro, 80 KB) | Go binary (27.9 MB) |
|---|---|---|
| PIE | enabled | disabled |
| NX stack | enabled | enabled |
| RELRO | enabled | disabled |
| Stack protector | enabled | unknown |
| Fortify | enabled | unknown |
| CET IBT and SHSTK | disabled | disabled |
| Stripped | yes | no |
The distro binary looks the way a hardened Debian build should. The Go binary is position-dependent with no RELRO and keeps its symbol table. The “unknown” rows are where rea is careful: it says no __stack_chk_fail or fortify symbol was found in the dynamic symbol table, and that a static binary may not show them. Go doesn’t use those C mechanisms at all, so unknown is the honest answer rather than a failure.
What the Release Exposure Audit Missed
Next I ran audit-release-exposure on the same Go binary. It’s meant to report what someone could recover from a shipped artifact, such as source maps, embedded sources or package metadata.
by_status: exposed 0, not_observed 5, not_applicable 6, unknown 1, not_assessed 3
no_exposure_observed_in_assessed_checks: true
I expected it to flag the full symbol table, since the hardening check had just reported the binary unstripped. It didn’t, because none of its 15 checks look at that. Its own output says native hardening is “not assessed” and points you to inspect_binary_hardening instead. So “no exposure observed” means none in the checks it ran, and the checks list is the part to read. Run both commands together if you’re auditing a release.
What Still Needs Ghidra
Anything that reads code inside the binary. analyze /usr/bin/bwrap exited 1 in about two seconds with provider_unavailable, and listed the four engines it had tried: ghidra, hopper, ida and kuna. The message noted that no target-support refusal was reported, which means the file type was fine and the machine just lacked an engine. rea’s help text describes decompile and decompile-all the same way, as reads that go through Ghidra or another provider.
To set that up, install Ghidra yourself, since rea won’t download it, then point rea at it and re-check.
export GHIDRA_INSTALL_DIR=/absolute/path/to/ghidra_12.1_PUBLIC
npx -y rea-agents@6.9.0 doctor
rea setup can register the MCP server in the coding tools it detects, and doctor already looks for a Cursor config. I didn’t run setup on this box, because it writes to agent config files. If you do, read what it plans to change first.
Should Your Agent Get These Tools?
For triage, yes. A hardening check or release audit is read-only, fast and returns evidence your agent can cite instead of guessing. That’s a good fit for a reviewer agent checking a vendor binary or your own release build. If you’re checking a third-party plugin before installing it, the habits in how to check a Claude Code mod is safe still come first, and a hardening report adds one more data point.
The bigger families need more care. Commands like debug-with-gdb, capture-process and the desktop capture tools run things, and rea’s own capabilities command lists side effects per provider. Give an agent those inside a sandbox, the way the coop sandbox for Claude Code does, not on your main machine. If you’re new to how an agent decides which tool to call, the learn-claude-code walkthrough explains the loop, and CLI-Anything vs computer use covers why a command-line tool is often the safer interface.
If you live in Ghidra’s own window, renaming variables and fixing types by hand, none of this replaces that. What rea 6.9.0 adds without any engine is a quick, sourced first look, and a clear error when the question needs more than headers.
4 comments